esFirmware (Physical Attacks Emulation)

esFirmware (Physical Attacks Emulation)

esFirmware is a physical attacks emulation tool that tests embedded software without a lab bench or physical chip. It simulates side-channel leakage and fault injection on your firmware binary. This lets you check countermeasures before silicon exists or without using the lab.
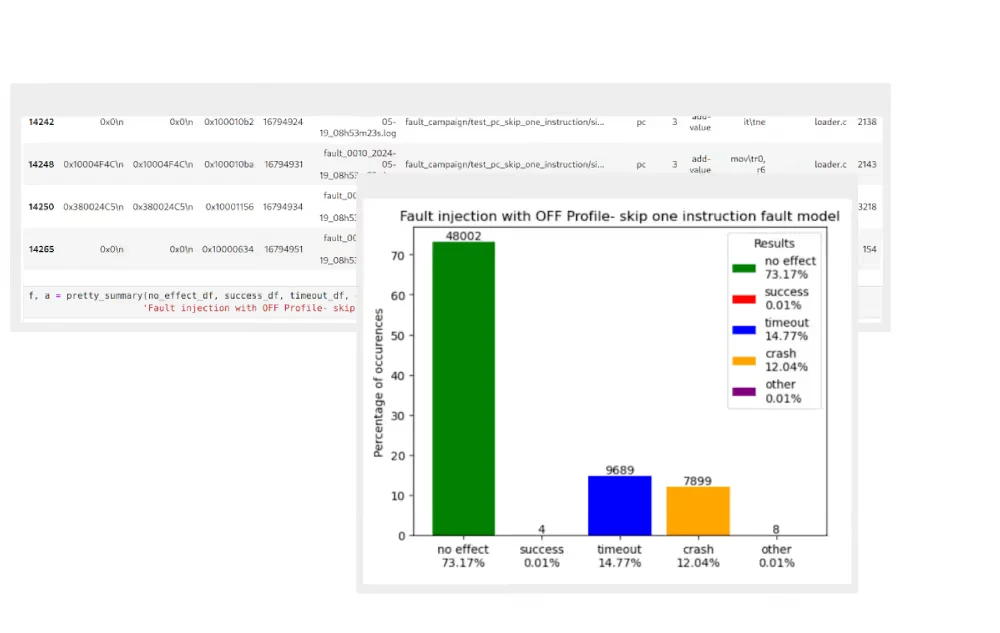
esFirmware physical attacks emulation by eShard

Why emulate physical attacks

Bench testing needs hardware, time and expertise. Many weaknesses are already visible in the code. Examples include a check that a single skipped instruction can bypass or a cryptographic routine that leaks information through its data. esFirmware finds these weaknesses early, when they cost the least to fix. It also lets you test again after every code change.

What's inside

  • Tracer engine: records execution and produces noise-free traces to validate AES, RSA, ECC and other cryptographic implementations
  • Fault injection engine: inserts faults at exact points in execution to simulate physical attacks and automate test campaigns
  • Root cause analysis: maps a vulnerable instruction back to its source code line
  • Ready-made notebooks: Jupyter notebooks for campaign setup, attack tutorials and leakage analysis. You can export trace datasets
  • Your own fault models: add custom fault models in Python and stub proprietary IP in C
  • CI/CD support: compile Python test campaigns into standalone executables that run in your build pipeline

Supported architectures

Intel x86/x64, Arm32/Arm64 and RISC-V.

Deployment

Runs on-premise as a ready-to-use JupyterLab instance on the esDynamic platform.

Typical uses

  • Pre-silicon validation of countermeasures
  • Regression testing of security code on every release
  • Reproducing a fault found on the bench and identifying its root cause, without booking lab time

Documentation

No public PDF. Pertech can send the catalogue on request.

Questions and answers

What is esFirmware?

esFirmware is eShard's physical attacks emulation tool. It runs side-channel and fault-injection tests on firmware in emulation, without a lab bench or physical hardware.

Can I test fault-injection countermeasures before silicon is available?

esFirmware lets you test fault-injection countermeasures before silicon is available. It emulates the firmware and injects faults in software to validate countermeasures.

Which architectures does esFirmware support?

esFirmware supports Intel x86/x64, Arm32/Arm64 and RISC-V.

Can esFirmware run in a CI/CD pipeline?

esFirmware supports CI/CD pipelines through Python test campaigns compiled into standalone executables. These executables run as part of your build and test pipeline.

Does esFirmware replace a physical lab?

esFirmware does not replace a physical lab. It catches software-level weaknesses early and at low cost. Physical effects specific to the silicon still need bench testing with eShard's side-channel and fault-injection labs.

Do I need esDynamic to run esFirmware?

esFirmware requires esDynamic and runs as a JupyterLab instance on that platform.

Where can I buy esFirmware in Israel?

You can buy esFirmware from Pertech Embedded Solutions, eShard's partner in Israel.

© 2025 Pertech Embedded Solutions Ltd. All rights reserved. By using this website you acknowledge and agree to our data practices. Personal information collected is used solely for providing sales, licensing, and technical support services. We do not sell personal data to third parties. View our full Privacy Policy.

upbtn
Skip to content