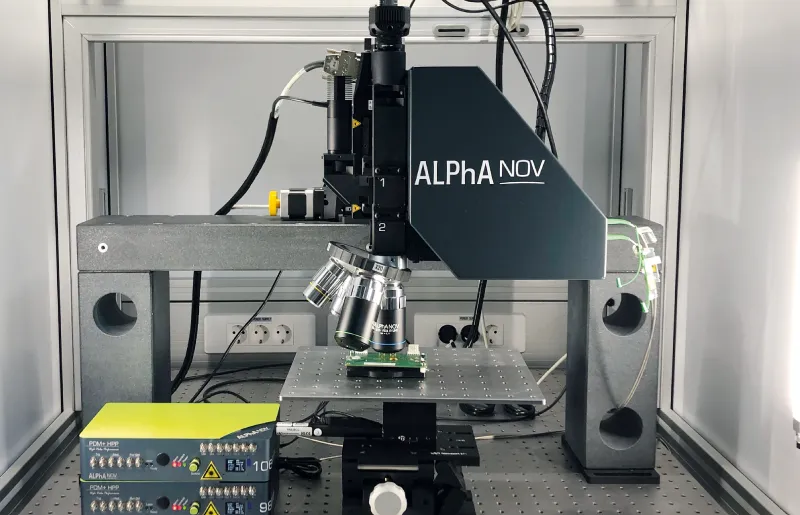
eShard’s laser fault injection (LFI) lab directs a focused laser pulse at a precise point on a chip at a precise moment. It tests whether the chip’s security countermeasures hold. The lab combines an ALPhANOV laser microscope station, triggering hardware and the esDynamic platform in one turnkey setup. It covers the full campaign, from imaging the die to exploiting the fault.
When light of the right wavelength hits a transistor, it creates a short burst of current. A precisely aimed burst can flip a bit in a register, corrupt a value in memory or make the processor skip an instruction. Attackers use this to bypass security checks, unlock debug access or recover cryptographic keys through differential fault analysis.
Laser fault injection is the most targeted of the common fault-injection methods. EM pulses and voltage glitches affect a wide area or the whole chip. A laser focused to about a micrometre can hit one logic block at one clock cycle. Evaluators of secure elements, smart cards and security ICs rely on this precision. Chip designers use it to test their countermeasures.
Several layers of metal wiring cover the front of a modern chip and block light. Silicon lets infrared light through. Most LFI campaigns therefore open the package from the back. Analysts image the die through the silicon with an infrared camera and fire the laser from below. eShard's laser station transmits more than 90% of the infrared light for backside injection.
esDynamic controls the equipment and supports analysis through each phase:
→ Full list: eShard Lab Equipment
esDynamic controls the lab equipment and keeps campaign work in one workspace:
Modern secure chips are designed to detect a single fault. They duplicate computations, check results, or use light and glitch sensors that reset the chip when they detect a problem. Evaluations now use double-fault attacks to test these protections. The first pulse bypasses a check or silences a sensor. The second performs the attack, such as skipping an instruction or flipping a bit. With up to four stacked lasers, eShard's lab can place faults at different points on the die and at different moments in the same run.
Secure elements, smart cards, ASICs, SoCs and FPGAs.
eShard also offers hardware security assessments against LFI for secure elements, ASICs, SoCs and FPGAs. It delivers replayable notebooks you can rerun on your own bench. Training runs remotely or on-site, from basic fault theory to fully automated multi-fault campaigns. Pertech arranges both in Israel.
Pertech is eShard's partner in Israel. We help define the lab around your targets and evaluation goals. We coordinate configuration with eShard and ALPhANOV, arrange installation and training, and support your team locally.
Laser fault injection (LFI) fires a focused laser pulse at a precise point on a chip, usually through its back side, to cause a controlled fault. It tests whether the chip's security countermeasures detect or block the fault.
eShard's Laser Microscope Station, powered by ALPhANOV, reaches a 1 µm spot size. It provides more than 90% infrared transmission for backside injection.
Metal layers on the front of a modern chip block light. Silicon lets infrared light through, so the back side gives direct optical access to the transistors.
Laser fault injection is far more localised than EM fault injection. A laser focused to about a micrometre can target one logic block, while an EM pulse affects a wider area. LFI usually needs the die exposed from the back; EM fault injection does not.
Yes. eShard offers hardware security assessments of secure elements, ASICs, SoCs and FPGAs against LFI, delivered with replayable notebooks you can rerun on your own bench. Pertech can arrange this in Israel.
eShard's LFI lab supports multi-fault attacks with up to four stacked lasers. It can place faults at different points and different moments in the same run.
Modern secure chips are built to detect a single fault. In a double-fault campaign, the first fault bypasses a check or silences a sensor and the second performs the attack. eShard's LFI lab supports this with up to four stacked lasers.
eShard's LFI lab offers sub-nanosecond timing, with an option for 10 ps trigger resolution using the Tombak trigger specialist. It also offers 1 µm spatial resolution. The Tombak option lets it target specific clock cycles on fast targets.
esDynamic controls third-party cameras, stages and oscilloscopes alongside eShard and ALPhANOV equipment. It is hardware-agnostic and also controls third-party pulse generators.
eShard's Laser Microscope Station is powered by ALPhANOV, a French optics and laser technology centre. The station is integrated into eShard's turnkey lab.
You can buy eShard's laser fault injection lab from Pertech Embedded Solutions, eShard's partner in Israel. Pertech handles configuration, installation, training and support.