The esReverse reverse engineering platform from eShard combines static analysis, full-system time travel debugging and AI agents. It provides a shared workspace that runs on your own servers. Security teams use it to analyse binaries, firmware, mobile apps and whole operating systems. Analysts can work together on an investigation and keep their findings for future work.
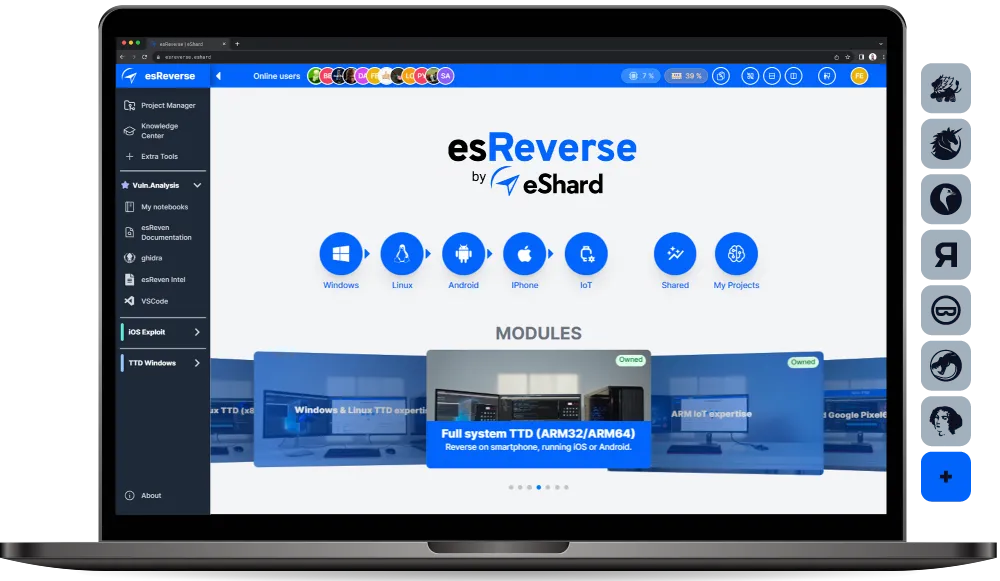
Most reverse engineering still happens one analyst at a time. Each person has a disassembler, a debugger, scripts and a notes file. That works for a single binary. It becomes harder when the target is a full system, several people need to investigate it, or similar questions return every few months.
Three problems recur:
esReverse addresses these three problems. It provides a shared workspace and combines static analysis with a full recording of system execution. Its AI runs inside your network.
An esReverse investigation follows these steps:
Every investigation is a project. Analysts can work on the same project at the same time, from creation to archive. Administrators use dashboards to manage shared resources, users and access centrally. Findings and workflows stay in the project, so teams retain knowledge after a project ends.
esReverse works with the tools analysts already use. It connects to Ghidra, IDA, Binary Ninja, GDB, Frida, BinDiff, VS Code and JupyterLab, along with Epoch and eShard's emulators. Teams can also connect in-house tools, add their own scripts and build custom workflows.
Epoch records a system's full execution in a deterministic trace. It saves every instruction, memory change and register state. Analysts can move forwards and backwards, jump to any instruction and inspect memory at any point. They can also follow data with taint analysis. The recording never changes, so analysts can replay race conditions and kernel panics as often as needed. → Time Travel Debugging (Epoch)
esReverse includes eShard's emulators, so analysts can study targets in a virtual environment, including iOS and Android virtual devices. When a real device is needed, an analyst can connect a physical mobile device over SSH and work with it using tools such as Frida and ADB.
Findings, scripts and workflows stay with each project, so the next investigation starts from what the team already learned. eShard also publishes expertise material for esReverse, such as advanced Intel techniques and IoT use cases.
esReverse treats AI as another project tool:
For organisations that can't use cloud AI, eShard offers a private language model that runs entirely on their infrastructure. No code, trace or finding has to leave the site. Three tiers are available, with regular model updates:
| Private LLM tier | Suited to | Comparable open models (per eShard) | Context window | GPU memory |
|---|---|---|---|---|
| Essential | Prototyping, light workloads | Qwen 3.6-27B, Gemma 4 | 256K tokens | under 100 GB VRAM |
| Professional | Production workloads at scale | DeepSeek Flash, GLM-4.7-Flash | 1M tokens | under 800 GB VRAM |
| Frontier | Largest model, heaviest workloads | GLM-5.2, DeepSeek-V4 Pro, Kimi K3 | 1M tokens | about 1.5 TB VRAM |
eShard has published several worked examples. Two show how AI agents use full-system traces:
The same approach applies to mobile apps. In another example, eShard recorded a banking app's launch and login in a full-system Android environment. The recordings contained about 4.8 and 2.3 billion instructions. It then asked an AI agent to report against the OWASP MASVS checklist. eShard describes this as an experiment, not a full assessment.
esReverse connects to IDA Pro and Ghidra. The table shows what it adds to these tools.
| Standalone disassembler (e.g. IDA Pro, Ghidra) | esReverse | |
|---|---|---|
| Static analysis | Yes | Yes, through the tools you already use |
| Full-system time travel debugging (kernel, drivers, all processes) | Not built in | Yes, with Epoch |
| AI that queries execution traces | Not built in | Yes, project-scoped agent |
| Private, on-premise LLM supplied with the platform | Not included (third-party plugins only) | Yes, three tiers |
Pertech is eShard's partner in Israel. We help define your setup and arrange a demo or evaluation on your own targets. We also size the servers and GPUs for the Private LLM, install the platform on your network, including air-gapped sites, and support your team after deployment.
The esReverse reverse engineering platform is an on-premise product from eShard. It combines static analysis tools, full-system time travel debugging and AI agents in a shared workspace for security teams.
Agentic reverse engineering in esReverse means using AI agents as investigation tools. An agent can join a project, search a recorded execution trace, inspect memory and registers, and tag findings for an analyst to verify.
esReverse connects to IDA Pro and Ghidra rather than replacing them. It also connects to Binary Ninja and other tools analysts already use. It adds time travel debugging, AI that queries execution traces, and shared projects.
esReverse can use AI on your own servers without sending code to the cloud. It can run a private LLM in one of three tiers or connect to an AI agent you already host. No data has to leave your network.
The esReverse Private LLM needs under 100 GB of GPU memory for Essential, under 800 GB for Professional, and about 1.5 TB for Frontier.
esReverse analyses Intel and Arm targets running Windows, Linux, Android or IoT firmware. It also supports iOS and Android targets through eShard's virtual devices.
Yes. With esReverse, an analyst can connect a physical mobile device over SSH and work with it using tools such as Frida and ADB. eShard's iOS and Android virtual devices are an alternative when no phone is at hand.
esReverse lets several analysts work on the same investigation at once. Each investigation is a shared project, and its findings, tags and scripts stay with it.
esReverse helps with malware analysis by using Epoch to record everything a sample does across the whole system. This includes code it downloads or decrypts at runtime. Analysts can then replay and study the recording safely.
esReverse can run on an air-gapped network without internet access. It installs on-premise with Docker or as a virtual appliance.
esReverse is licensed per server, with no limit on the number of users in a project. The Project Manager, which oversees many projects, is licensed separately. Pertech provides quotes in Israel.
esReverse is eShard's reverse engineering platform, while Epoch is its time travel debugging tool. Epoch runs on esReverse.
You can buy esReverse from Pertech Embedded Solutions, eShard's partner in Israel. Pertech also handles demos, installation, onboarding and local support.